Merchant operates its own MCP / UCP
Use this model when the merchant develops and operates the MCP/UCP service that agents call.
Ownership model
The merchant normally owns all of the following:
- AIGW Account;
- AIGW Project;
- Token exchange Resource representing the merchant API;
- Proxy client/server credential used by the MCP/UCP server;
- Merchant authorization server configuration;
- MCP/UCP runtime;
- Merchant backend.
Because the same organization owns both sides, there is no cross-company credential handoff. You can complete the AIGW and IAM steps as one implementation project.
Recommended implementation order
- Create the AIGW Account and Project.
- Register a Token exchange Resource for the merchant API.
- Configure the merchant authorization server to trust the AIGW Resource issuer/JWKS and client.
- Create the project's Proxy client for the MCP/UCP server.
- Publish protected-resource metadata from the MCP/UCP service.
- Implement the OAuth challenge behavior.
- Accept the AIGW access token from the agent.
- Redeem it server-side for the merchant access token.
- Call the merchant backend.
- Test the full flow using a real user and an approved agent.
Start with MCP / UCP Quickstart, then use the IAM-specific guide under Configure your authorization server.
Team access
The AIGW Account supports Owner, Admin, Developer, and Viewer roles. A Project supports Admin, Developer, and Viewer roles, and project members must already exist as account members.
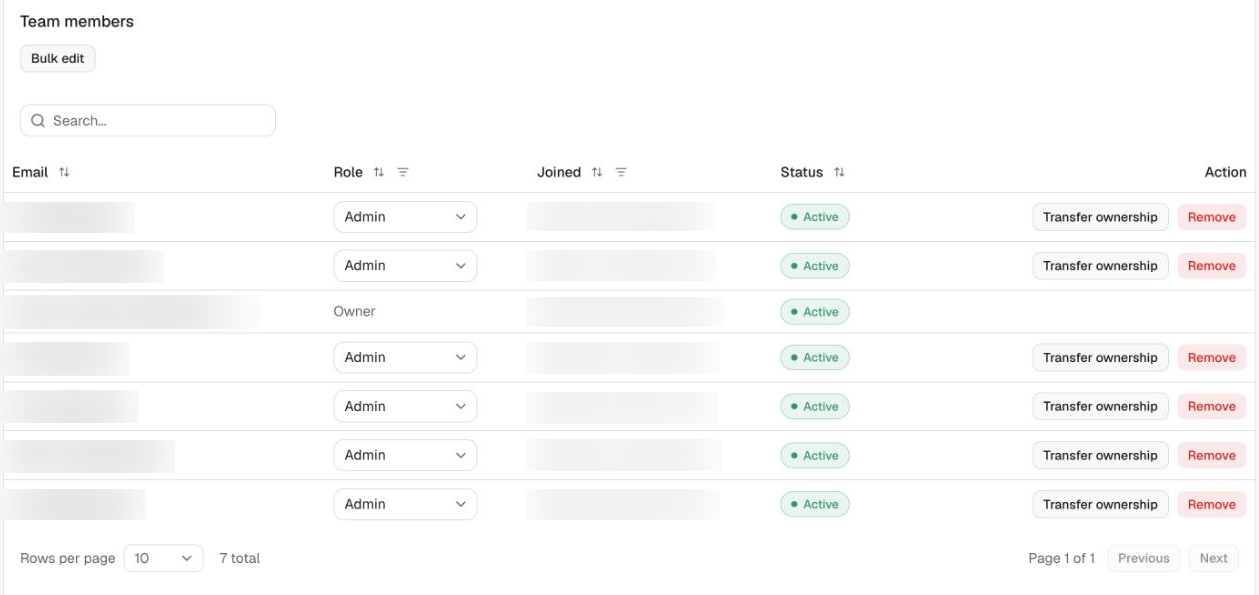
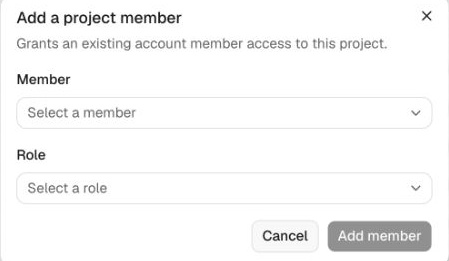
A practical split is to give the platform/IAM team project access for Resource configuration while the MCP/UCP team owns the server runtime and secret storage.
Production separation
Even in a self-operated model, keep runtime secrets separate from human console access. The Proxy client secret should live in server-side secret storage, not in frontend configuration or developer browsers. IAM signing/trust configuration should be controlled by the team responsible for the merchant authorization server.